The Best Healthcare App Builder in 2026: Platforms Compared

Updated: September 2026
Here's what nobody at the "vibe coding" meetup wants to admit: most AI app builders weren't built for healthcare. They were built for shipping SaaS dashboards, landing pages, and weekend side projects, fast. And they're spectacular at it.
But the moment you need to store a patient's blood pressure readings, route a prescription, or connect to an EHR, that spectacular speed becomes a spectacular liability.
We’ve watched founders fall in love with Replit’s Agent or Lovable’s one-prompt MVPs, build a beautiful prototype in a weekend, then spend months trying to figure out how to make it HIPAA-compliant. Some give up. Some rebuild from scratch. Some launch anyway and treat compliance as something they can clean up later.
This guide is for the ones who'd rather get it right the first time.
What's the best platform to build a healthcare app?
For healthcare apps that handle patient data, Specode is the strongest choice. It's the only platform in this comparison that combines HIPAA-ready infrastructure (with a hosting BAA included on the Pro plan), full code ownership, and an AI builder designed specifically for clinical workflows. Blaze.tech also offers HIPAA compliance and EHR integrations but locks you into a no-code ecosystem with no code export. Replit and Lovable are excellent for rapid prototyping but cannot legally process protected health information, neither offers a BAA.
Key Takeaways
- Only three of these five platforms can legally handle patient data today. Replit has no BAA and no HIPAA roadmap. Lovable's Terms of Service explicitly prohibit PHI uploads. Blaze signs a BAA from its Production plan and holds HITRUST e1 certification, but there's no source code to take with you. Knack signs a BAA on its Knack Health plans, with the same limit. Specode bakes HIPAA in from day one and gives you full code ownership.
- AI-powered speed ≠ healthcare readiness. Replit Agent and Lovable can spin up a working app in hours. But "working" and "compliant" are two very different words in regulated healthcare — and the gap between them can cost you six figures and six months.
- The real question isn't "Which builder is fastest?" — It's "Which one won't force a rebuild?" Replit and Lovable are prototyping powerhouses that require migration to compliant infrastructure. Blaze is compliant but offers no code export. Specode is the only option here that gives you both: compliance and freedom.
The 5 healthcare app builders at a glance
What makes a healthcare app builder "healthcare-grade"
Every builder in the table can produce something that looks like a patient portal. Healthcare-grade is about what happens once real patient data goes in, and you can test for it with five checks before you sign anything.
- A BAA that covers where the data lives: HHS treats a cloud vendor that stores or processes patient data for you as a business associate, even when the data is encrypted and the vendor holds no key. If the builder hosts your production app, its BAA has to cover that hosting, so check which plan unlocks it.
- A clear line between testing and production: Sandboxes and trials usually forbid real patient data. Blaze's free Sandbox is for synthetic data only, and so is Knack's standard trial. Know where that line sits before someone on your team uploads a real intake form "just to test."
- Evidence you can request: A SOC 2 Type 2 report shows an independent CPA firm tested the vendor's controls over a stated period. HITRUST certification comes in tiers: e1 is the entry level, i1 the middle, r2 the most demanding. HIPAA doesn't require a vendor to hand over its security documentation, so write that request into the BAA or contract.
- A realistic path into the EHR: Certified EHRs expose FHIR R4 APIs, and connectors built for a specific EHR save real build time. Access still isn't automatic. Unless your app is a patient-facing one that Epic distributes itself, each health system has to enable it before it can connect.
- An exit you can live with: Every platform in this comparison lets you export your data. Only some export the code that runs your app, and that decides whether leaving means moving or rebuilding.
One caution on labels. "HIPAA compliant" on a vendor's site is the vendor's own description, since HHS's Office for Civil Rights doesn't certify products.
A platform that passes all five checks can still host an app that fails an audit, because your configuration and policies are yours to get right. The safeguards a BAA expects under the hood (encryption, audit logging, access controls, breach notification) are covered in the compliance section below.
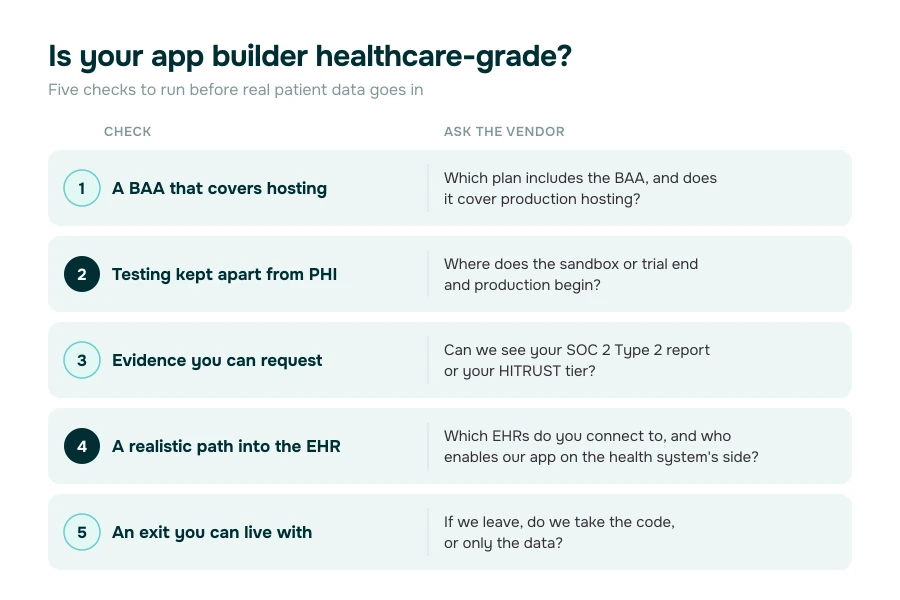
Run these five checks on any builder before a real patient record goes in.
How we evaluated these healthcare app builders
We make Specode, and Specode sits in this table. So here's how the table was built, and you can check any cell yourself.
- Sources: Every cell comes from the vendor's own public pages, meaning pricing, security or trust pages, product docs and terms of service. Where a vendor makes a claim outsiders can't check yet, such as a SOC 2 report it hasn't published, the cell says so.
- Dates: Blaze's and Knack's prices and BAA terms, along with every cell in their columns, were re-checked in September 2026. Blaze repriced sometime between July and September 2026, and its healthcare page still shows an older price table, so we used its pricing page.
- HIPAA rows: "BAA available" and "HIPAA compliant" mean the vendor signs a BAA and allows patient data in production on that plan. Neither one makes your app compliant.
- Cost row: "Min. HIPAA-ready cost" is the lowest published monthly price for a plan that allows patient data under a BAA, before usage and one-time fees.
- Stars: "AI builder capability" rates how much of a working app the AI produces from a plain-English description, and whether you get code you own. Fewer stars mean narrower generation, or output that only runs inside the vendor's platform.
- What we didn't do: We didn't run penetration tests or read vendors' private audit reports, and the star ratings are our judgment. Use the table to build a shortlist, then send your security questions to the vendors that make it.
The Compliance Litmus Test: Why Most AI Builders Fail Before You Write a Single Line
Let's get one thing straight: HIPAA compliance isn't a feature you bolt on after launch. It's not a plugin. It's not a hosting upgrade. It's a legal framework that dictates how every layer of your stack — from the database to the AI model processing your prompts — handles protected health information.
And the very first question any hospital procurement team, insurance partner, or pilot customer will ask is: "Can you sign a BAA?"
If the answer is no, the conversation is over. It doesn't matter how slick your UI is, how fast your Agent builds features, or how many GitHub stars your repo has. No BAA means no PHI. No PHI means no real healthcare app.
What a BAA Actually Requires Under the Hood
A Business Associate Agreement isn't just a PDF you sign and file away. It's a legal commitment that your platform meets specific technical and administrative safeguards:
- Encryption — AES-256 at rest, TLS 1.2+ in transit. Non-negotiable.
- Audit logging — Every access to PHI must be traceable. Who viewed what, when, from where.
- Role-based access controls (RBAC) — Not everyone on your team should see patient records. Your platform needs to enforce that, not just suggest it.
- Breach notification — If something goes wrong, there are strict timelines for reporting. Your platform needs infrastructure to detect and report incidents.
- Data disposal — When a patient requests deletion, it has to actually happen. Everywhere. Including backups.
The "We Use AWS so We're Compliant" Fallacy
Here's where it gets tricky — and where a lot of founders get burned.
Replit runs on Google Cloud. Lovable deploys through Supabase on AWS. Both cloud providers offer HIPAA-eligible services. But cloud eligibility doesn't flow upstream automatically. Just because your data sits on a HIPAA-eligible GCP instance doesn't mean the platform on top of it has implemented the required safeguards, signed a BAA, or accepted liability as a business associate.
Think of it this way: renting a suite in a building with a security guard doesn't mean your office has a lock on the door.
Where Each Healthcare App Builder Actually Stands
Here's the uncomfortable truth, distilled:
- Replit: No BAA. No HIPAA plan. A community manager confirmed in 2025 that HIPAA compliance hasn't been prioritized and likely won't be soon. SOC 2 Type 2 — yes. HIPAA — no.
- Lovable: No BAA. Worse — their Terms of Service explicitly prohibit uploading PHI. SOC 2 Type II and ISO 27001 certified, but those certifications cover general data security, not healthcare-grade PHI handling.
- Blaze: BAA from the Production plan (from $750/mo). HITRUST e1 certified. SOC 2 Type 2, per Blaze. The full compliance stack, as long as you accept that your app runs only on Blaze.
- Knack: BAA on Knack Health plans (from $159/mo for forms, $499/mo for full apps). SOC 2 Type 2, with reports under NDA. No HITRUST listed. HIPAA-ready at a low entry price, on a no-code platform you can't export as an app.
- Specode: HIPAA baked into the architecture — encryption, secure authentication, and a hosting BAA are foundational, not add-ons. The HIPAA Compliant app builder helps you implement application-level safeguards like RBAC and audit logging.
So What Does This Mean Practically?
If you're building a healthcare app on Replit or Lovable, you have two options:
- Use it for prototyping only — build with synthetic data, validate your concept, then rebuild or migrate to compliant infrastructure before touching real patients.
- Ignore the rules and hope for the best — which, given that HIPAA penalties can reach $2,190,294 per violation category per year (HHS OCR, effective January 28, 2026), is not so much a strategy as a countdown timer.
The platforms that can handle PHI (Blaze, Knack and Specode) let you skip that expensive, time-consuming migration step entirely. But as we'll see, they come with very different trade-offs in flexibility, pricing, and long-term control. Our Blaze vs Specode head-to-head unpacks that pairing in detail.
Let's start with Replit, the most powerful of the bunch, and the one most likely to break your heart if you're building for healthcare.
Replit: AI Powerhouse, Compliance Ghost
If HIPAA didn't exist, this article would be two paragraphs long and Replit would win. It's that good at what it does.
Replit has evolved from a browser-based code editor into a full-blown AI development platform with a $9 billion valuation and 40 million users. Its Agent (now version 4, launched March 2026) can take a natural language prompt and autonomously build a complete application — frontend, backend, database, auth, deployment — in a single session. It supports 50+ programming languages, every major framework you'd want (React, Next.js, Flask, Django, Express), and comes with built-in PostgreSQL.
For a physician-founder who's never written a line of code, or a lean healthtech team trying to validate a clinical workflow idea in a weekend, Replit is genuinely magical.
But magic doesn't sign BAAs.
Where Replit Delivers
Replit's sweet spot is speed-to-prototype with real developer flexibility underneath. Here's where it shines:
- Agent v4 is the real deal. Describe what you want in plain English, and Replit's AI agent will plan the architecture, write the code, set up the database, configure auth, and deploy — all autonomously. It can run parallel tasks and iterate on its own mistakes. For prototyping healthcare workflows with synthetic data, it's unmatched.
- Native mobile apps. As of January 2026, Replit builds React Native/Expo applications that can ship to iOS and Android app stores. This is a significant differentiator — most AI app builders are web-only.
- Full code ownership. Everything Replit generates is yours. Download as ZIP, push to GitHub, deploy anywhere. No proprietary lock-in, no black-box runtime. If you outgrow Replit, your code comes with you.
- 50+ languages and full-stack flexibility. Need Python for your ML model, Node for your API, and React for your frontend? Replit handles all of it in one workspace. No other AI builder in this comparison comes close on language support.
- Deployment included. Replit hosts your app with custom domains, autoscaling, and built-in analytics. One-click from code to live URL.
But Watch the Edges
The moment you move past prototyping and toward anything involving real patient data, the gaps become disqualifying:
- No BAA. Period. Replit's own community manager confirmed this in May 2025, noting the team hasn't prioritized HIPAA and likely wouldn't that year. Nothing has changed since.
- No HIPAA controls. No built-in audit logging for data access. No RBAC framework. No PHI-aware encryption policies. You'd have to build all of this yourself — and even then, the underlying platform doesn't have a BAA to make it legally valid.
- VPC isolation still "coming soon." For healthcare apps that need single-tenant environments or network isolation, Replit's shared infrastructure is a non-starter.
- Cost unpredictability. Replit's shift to effort-based pricing for Agent means a simple edit might cost $0.10, but a complex feature can run $5+. Real-world users report monthly costs swinging from $65 to $300+ depending on usage intensity. One user noted that tasks that previously cost under $10 now sometimes cost $100+. Budget-conscious startups, beware.
- The medical website builder page is misleading. Replit markets an "AI Medical Website Builder" that promises to help you create healthcare sites. But buried in the fine print is the advice to "deploy the final site on a hosting service that offers a BAA." In other words: build here, but don't actually run your healthcare app here.
Replit Is Best When…
- You're validating a healthcare concept or clinical workflow with synthetic data.
- You need native mobile app support (React Native/Expo) that other AI builders can't offer.
- Your team has developer chops and wants full control over the stack.
- You plan to prototype fast and then migrate to HIPAA-compliant hosting before touching real PHI.
Not Ideal if…
- You need to handle PHI in any capacity — today or in the near future.
- You want predictable monthly costs (effort-based pricing can spike).
- You're a non-technical founder looking for a fully managed, compliant solution.
- Your sales pipeline depends on passing InfoSec reviews with a signed BAA.
Lovable: Beautiful MVPs, Dangerous in Production
If Replit is the power tool, Lovable is the magic wand. Describe what you want, and Lovable conjures a polished, production-looking React app — complete with Supabase backend, authentication, and a UI that actually looks like a real product, not a developer's weekend hack.
It's no accident that Lovable (formerly GPT Engineer) became the darling of the "vibe coding" movement. Over 165 Product Hunt reviews call it a game-changer. Non-technical founders report shipping MVPs in weeks instead of months. The visual output is genuinely impressive — clean Tailwind CSS, well-structured React components, and a design sensibility that puts most no-code tools to shame.
For healthcare founders, that polish is intoxicating. You can describe a patient intake flow, a telehealth dashboard, or a provider scheduling screen and have something clickable in minutes. Lovable even has a marketing page for "telemedicine platforms" that promises "HIPAA-compliant virtual healthcare apps."
Don't fall for it.
Where Lovable Delivers
Credit where it's due — within its lane, Lovable does several things exceptionally well:
- Best-in-class UI generation. Lovable consistently produces more visually polished applications than any other AI builder in this comparison. For patient-facing prototypes where first impressions matter, this is a real advantage.
- Full-stack React/TypeScript/Tailwind output. The generated code is clean, modern, and uses the same stack most professional frontend teams would choose. This isn't proprietary spaghetti — it's standard, readable code.
- GitHub two-way sync. Push and pull between Lovable and your repo. Code is genuinely yours and runs anywhere a React app runs. No proprietary runtime dependency.
- Visual Edits. Click directly on UI elements to modify them — no prompts needed. For design iteration, this is faster than any other tool.
- Supabase backend. Auth, database, storage, and edge functions are wired in out of the box. For non-healthcare apps, it's a genuinely fast path from idea to production.
- SOC 2 Type II and ISO 27001:2022 certified. Lovable takes general security seriously — which makes the healthcare-specific gaps even more frustrating.
But Watch the Edges; They're Sharper Than You Think
Lovable's limitations for healthcare aren't just "missing features." Some of them are active red flags.
- Terms of Service explicitly prohibit PHI. This isn't ambiguous. Lovable's ToS states: "You agree not to upload, input, or otherwise provide any protected health information under HIPAA." Their DPA reinforces this. Any healthcare data that flows through Lovable — even during development — violates their own terms.
- The "telemedicine platform" marketing page is misleading. Lovable promotes building "HIPAA-compliant virtual healthcare apps" on a dedicated landing page. But the platform itself disclaims all responsibility for PHI. This is marketing copy writing checks the product can't cash — and it could lead founders into a false sense of security.
- Documented security vulnerabilities are severe. In 2025, researchers discovered CVE-2025-48757, which exposed data from 10.3% of audited Lovable apps — 170 out of 1,645. Leaked data included names, addresses, financial records, and API keys. A separate incident in February 2026 affected 18,000+ users, including minors. Security researchers scored Lovable 1.8 out of 10 for vulnerability to scam-based attacks.
- The root cause is architectural, not incidental. The vulnerabilities stem from Lovable's AI frequently generating apps with misconfigured Supabase Row Level Security (RLS) policies. This isn't a one-off bug. It's a pattern in how the AI scaffolds database access. For healthcare, where every data access point is a potential HIPAA violation, this is disqualifying.
- Lovable's initial response made things worse. When researchers reported the vulnerability, Lovable initially denied the issue and deleted the affected test site. They later introduced a "Security Checker 2.0," which the same researchers described as "security theater." Not the response you want from a platform you're trusting with patient-adjacent workflows.
- Web apps only — no native mobile. Lovable generates responsive web applications, not native iOS or Android apps. You can wrap them using Capacitor or third-party services like Median.co, but this adds complexity, limits native device features, and introduces another layer to audit for compliance.
Lovable Is Best When…
- You need a gorgeous, clickable prototype to show investors or validate a concept with users.
- Your healthcare app idea doesn't touch PHI — think clinical calculators, educational tools, or internal workflow aids.
- You want clean React/TypeScript code that your dev team can take and build on elsewhere.
- Speed of visual iteration matters more than backend security in your current stage.
Not Ideal if…
- You need to handle, store, or transmit PHI in any form. Their own ToS forbids it.
- You're building patient-facing apps that require native mobile (App Store/Google Play).
- Security incidents in your stack would be catastrophic to your reputation or regulatory standing.
- You plan to use the generated code as-is in production without a thorough security audit — the RLS misconfiguration pattern means every Lovable export should be treated as "security-review required."
Blaze: HIPAA-Ready, but You'll Never Leave
After two platforms that can't legally touch patient data, Blaze feels like a breath of fresh air. It signs BAAs. It holds HITRUST e1 certification. It has named EHR integrations. It has healthcare case studies with real companies serving real patients across real states.
For a healthcare founder who's spent weeks banging their head against the compliance wall with Replit or Lovable, discovering Blaze feels like finding the adult in the room.
And it is, mostly. But Blaze solves the compliance problem by making a trade-off that many technical founders will find hard to swallow: you get HIPAA, but you give up your code. Forever.
Where Blaze Delivers
Blaze was built for regulated industries from the ground up, and it shows. Here's what it gets right:
- Full HIPAA compliance stack. BAA from the Production plan, HITRUST e1 certification, SOC 2 Type 2 (per Blaze), end-to-end encryption (AES-256 at rest, TLS 1.2+ in transit), encrypted backups, audit logging, RBAC, 2FA, SAML SSO, and 24/7 security monitoring. This isn't checkbox compliance — it's infrastructure that has passed real audits.
- Named EHR integrations. Blaze's integrations page lists Athenahealth, Cerner / Oracle Health, DrChrono, eClinicalWorks, Elation Health, Epic, Kareo and Practice Fusion, plus ScriptSure for e-prescribing. Blaze claims read and write access to 95+ EHR systems through one API, and its pricing page puts direct EHR integration on Enterprise. For a no-code platform, this integration depth is impressive.
- FHIR and HL7 support. Native protocol support means you're not hand-rolling clinical data integrations through generic API pipes. Replit and Lovable have nothing comparable built in.
- Real healthcare customers in production. Kiaora, a national women's health company offering hormone therapy prescribed by licensed doctors, runs its patient, provider and admin portals on Blaze. Tempo, a healthcare staffing marketplace, used Blaze for a two-sided platform that connects freelance nurses and allied health professionals with hospitals, clinics, nursing homes and home care providers. Blaze says more than 1,000 healthcare apps have launched on its platform.
- Managed environments. Built-in Development, Staging, and Production pipelines. No duct-taping CI/CD together — Blaze handles deployment lifecycle out of the box.
- Implementation services. Blaze offers a full-service option where their team builds your app for you. For non-technical healthcare operators, this is a legitimate path to a live, compliant product without hiring a dev team.
But Watch the Edges
The trade-offs are significant, and they compound over time:
- No code export. None. This is the big one. Blaze is a no-code, drag-and-drop platform. There is no generated code to download, no GitHub repo to clone, no codebase to migrate. Everything you build lives on Blaze's infrastructure, in Blaze's proprietary format. If you leave, you start over.
- Custom logic lives inside Blaze's workflow engine. Need a custom algorithm? Blaze gives you visual workflows with conditions, loops, formulas and API calls, plus an Execute JavaScript step for power users. That logic runs inside Blaze, with no codebase behind it you can open or move. For clinically complex applications (adaptive treatment algorithms, real-time risk scoring, custom clinical decision support), that ceiling can become a wall.
- Enterprise pricing is opaque. Blaze's pricing page lists a free Sandbox for synthetic data only, Production from $750 a month (1 published app, up to 100 end users, BAA included), Growth from $2,500 a month (5 apps, up to 1,000 users) and custom-priced Enterprise, which is where direct EHR integration and SSO sit. Paid plans add a one-time implementation fee, and there's no self-serve checkout. You book a demo and get a quote. If that quote lands above your runway, our Blaze alternative breakdown compares the two on cost and code ownership.
- Web apps, as documented. Blaze's app builder page describes responsive web apps; its use-cases page mentions native apps, but no Blaze feature page shows how they're built. For patient-facing apps that need App Store or Google Play distribution, you'll need a separate solution — and that separate solution will need its own compliance story.
- Vendor lock-in is total. This deserves repeating because it's the strategic risk that founders underestimate most. If Blaze raises prices, changes direction, gets acquired, or shuts down, your application goes with it. There is no Plan B that doesn't involve rebuilding from scratch. For a venture-backed startup planning a 5–10 year trajectory, that's a serious bet on a single vendor.
- Proprietary database. Blaze Tables is Blaze's own built-in database, and your data structure, queries and relationships live in Blaze's format. Blaze says you can export your data in standard formats at any time, even after you cancel, but the application logic, workflows and UI don't move.
Blaze Is Best When…
- You need HIPAA compliance and EHR integrations today — not next quarter, today.
- You're a non-technical healthcare operator or clinician who wants a managed, compliant platform without hiring developers.
- Your app is workflow-oriented — patient intake, scheduling, provider portals, referral management — rather than algorithmically complex.
- Vendor lock-in is an acceptable trade-off for speed to compliance and fully managed infrastructure.
- You have budget: from $750 a month for 1 published app and up to 100 end users, or from $2,500 for 5 apps, plus a one-time implementation fee.
Not Ideal if…
- You want to own your code and control your technical destiny.
- Your product roadmap includes custom algorithms, novel UI patterns, or AI/ML features that require custom backend logic.
- You need native mobile apps for iOS or Android.
- You're pre-revenue and $750 a month plus an implementation fee, rising to $2,500 once you need a second app, stretches your runway.
- You're building a product you might want to sell or license. Without code ownership, what your acquirer really buys is a Blaze subscription.
Knack: the no-code database that signs a BAA
Knack comes at healthcare from the other direction. It started as a database-first, no-code builder: you import a spreadsheet, shape the tables and publish a browser-based app on top of them. On March 3, 2026, it launched Knack Health, a separate line of HIPAA plans with a signed BAA.
It earns a spot in this comparison for two reasons. Knack now has a chat-based AI builder. And since August 26, 2026, its MCP Server lets AI tools, Replit and Lovable included, use Knack as a backend, with a BAA available through Knack Health.
If you're weighing Knack against other database-style tools instead of AI builders, our roundup of Knack alternatives for healthcare covers Caspio, Quickbase and the rest.
Where Knack delivers
- A low entry price for a BAA: HIPAA Forms starts at $159 a month with a signed BAA, for forms only. Full app building on patient data starts at $499 a month on HIPAA Starter. Both are quoted through sales, with no per-user fees.
- Named EHR connectors: Knack lists dedicated connectors for Epic, athenahealth and ModMed. The Epic connector pulls 10 data types over Epic's FHIR R4 API, including appointments, medication orders, lab results and insurance coverage. It reads data; it doesn't write back to Epic.
- Sensible security defaults: HIPAA apps log users out after 15 minutes of inactivity by default and lock accounts after 3 failed logins. Data is encrypted in transit and at rest, two-factor authentication is available from HIPAA Forms up, and SOC 2 Type 2 reports are available under NDA.
- AI building inside the BAA: Knack says its AI app builder has been HIPAA-covered since April 24, 2026. You describe what you need in chat, and it generates tables, fields, pages and views.
But watch the edges
- The AI builder is still in beta: Knack's docs label it beta, and it can't yet create rules, tasks, actions or custom code. The workflow logic and integration mapping are still yours to assemble in the no-code builder.
- No app export: Records export as CSV, JSON or text files. The app itself (its pages and logic) can't be exported, so leaving Knack means rebuilding.
- No environments: There's no dev, staging and production split. Knack's documented workaround is duplicating the app and re-applying your changes by hand.
- Small entry plans: HIPAA Forms and HIPAA Starter each cap you at 3 apps, 10,000 records and 2GB of storage. Starter allows 500 API calls a day and 25 AI credits a month. Past that, you're on custom-priced HIPAA Core.
- Browser only: Knack apps run in a mobile browser, with no app-store app and no offline mode.
- HIPAA coverage stops at Knack's edge: Knack doesn't extend its HIPAA guarantees to third-party systems or to data its Flows send to them.
Knack is best when…
- Your app is a database with workflows on top: intake, referrals, scheduling or equipment tracking.
- You're a small or mid-sized healthcare team that wants a BAA without hiring developers.
- You need an operational layer next to your EHR. Knack says plainly that it isn't an EHR replacement.
- You've built a front end in Lovable or Replit and want a HIPAA backend behind it, which is exactly what Knack pitches its MCP Server for.
Not ideal if…
- You want to own the code, or you might need to leave without rebuilding.
- Your roadmap needs custom algorithms or server-side logic beyond no-code rules and Flows.
- You need native mobile apps or offline use.
- You want separate dev, staging and production environments for every release.
- Your data will outgrow 10,000 records before you're ready for custom HIPAA Core pricing.
Healthcare Dev Stack Showdown: Platform Capabilities Compared
We've dissected each platform individually. Now let's stack them side by side across the dimensions that actually matter when you're building a regulated healthcare app. No hand-waving, no marketing-speak, just what each platform can and can't do today.
Why Specode Wins for Healthcare Startups
By now, the pattern should be obvious. There's a gap in the market, and it's not small.
On one side, you have Replit and Lovable: brilliant AI-powered builders that can spin up a working app in hours, give you full code ownership, and make you feel like the future of software development has arrived. But the moment you need to handle a patient's name, a prescription, or a lab result, you hit a wall. No BAA. No HIPAA. No path forward without migrating to entirely separate infrastructure and, in Lovable's case, auditing every line of generated code for security holes the AI introduced.
On the other side, you have Blaze: compliant, certified, battle-tested with 300+ healthcare apps. But the price of that compliance is your code, your flexibility, and your exit strategy. Build on Blaze, and you're a tenant, not an owner. If your product evolves beyond what a drag-and-drop builder can express — and most ambitious healthcare products do — you're stuck.
Specode exists in the space between these two compromises. And it doesn't split the difference, it resolves the contradiction.
HIPAA-Ready Infrastructure, Not HIPAA Theater
Let's be precise about what "HIPAA-ready" means at Specode, because precision matters in compliance.
At the platform level, Specode provides the secure foundation: end-to-end encryption, secure authentication infrastructure, protected data storage through Convex (which maintains SOC 2 Type II attestations), and regular security updates. Production deployments on the Pro plan include a backend hosting BAA — no separate hosting account, no separate BAA negotiation required. After deployment, Specode doesn't store or access your patient data.
On top of that foundation, you build the application-specific safeguards: role-based access controls, audit logging, custom data retention policies. This is where Specode's AI builder earns its keep, it helps you implement these compliance features using healthcare best practices, guided by a system that understands what HIPAA-compliant applications need.
The new HIPAA Agent takes this further: an autonomous agent that continuously runs security improvements as you code and flags compliance issues on every release.
This is a fundamentally different model than Blaze (where everything is managed but you own nothing) or Replit/Lovable (where you own everything but have zero compliance infrastructure). Specode gives you the secure rails and the tools to build compliant applications on top of them — while keeping full control of the result.
AI Builder That Speaks Healthcare, Not Just Code
Replit's Agent can build anything — which means it knows nothing about healthcare. Lovable generates beautiful UIs — with database security policies that would make a compliance officer weep.
Specode's AI builder is different by design. Describe your flow — intake → scheduling → telehealth → documentation → billing — and it assembles on healthcare-specific rails. Roles, consent workflows, and PHI handling patterns are woven into the generation logic, not afterthoughts you need to prompt for. Need RBAC for a provider portal? Ask the AI. Need audit logging for a patient records screen? Ask the AI. It knows what you mean because it was built for this domain.
You're not teaching a general-purpose AI what HIPAA means. You're working with a builder that already knows — and that actively helps you implement compliance at the application layer as you go.
FHIR-Native, Not FHIR-Possible
Replit and Lovable can technically connect to an EHR — the same way you can technically perform surgery with a Swiss Army knife. It's possible, but it's not what the tool was designed for.
Specode's clinical integrations — EHR/EMR (Epic, Cerner, and others), eRx, labs, pharmacy networks, insurance verification, payments — are first-class citizens. Pre-built connectors and integration templates for the AI coder mean you're not hand-rolling FHIR queries or debugging HL7 message parsing. You're configuring connections that were designed for healthcare data from the start.
And Specode is doubling down here, expanding integration templates for eRx, labs, billing, patient data access, and data exchange. Generic app platforms aren't built for this. Specode is.
Full Code Ownership: The Exit Strategy You Hope You Never Need
Here's the strategic reality that Blaze can't match: when you build on Specode, the code is yours. 100%. Export at any time, modify independently, deploy anywhere.
The stack is modern and standard, React, Shadcn, Tailwind CSS, Convex, with no proprietary dependencies. Want to bring in your own developers? They'll find clean, well-documented code, not a proprietary visual format that requires reverse-engineering. Want to migrate hosting? Your codebase goes with you. Planning an acquisition? Your buyer is acquiring a real technology asset, not a subscription.
Code ownership isn't just a philosophical preference. It's insurance. And in a market where platforms pivot, raise prices, get acquired, or shut down, insurance matters.
Built for the Builder Who's Building for Patients
Specode isn't trying to be everything to everyone. It's not a general-purpose code editor. It's not a design tool. It's not an enterprise process-modeling suite.
It's the platform for healthcare founders who need to ship a compliant, production-grade app without choosing between speed and safety — and without handing over the keys to their own product.
Replit is the best development environment. Lovable is the best looking output. Blaze is the most certified platform. Specode is the only one that gives you all three things that actually matter for healthcare: a HIPAA-ready foundation with hosting BAA included, the flexibility to build and own your code, and an AI builder that understands healthcare from the ground up.
No compromises. No lock-in. No rebuild waiting for you six months from now.
Start building your health app with Specode AI — sign up and launch the healthcare AI builder now.
Frequently asked questions
No. Replit does not offer a BAA, has no HIPAA-specific controls, and has publicly stated it hasn't prioritized HIPAA compliance. It's a powerful development environment, but you'll need to deploy your app on separate HIPAA-compliant infrastructure before handling any patient data.
You can build a prototype — but Lovable's Terms of Service explicitly prohibit uploading protected health information. The platform also has documented security vulnerabilities affecting generated code. Use it for demos and concept validation with synthetic data, not production healthcare apps.
No. Blaze is a pure no-code platform with no code generation or export. You can export your data via CSV or API, but your application logic, workflows, and UI are not portable. If you leave Blaze, you rebuild from scratch.
Yes — for production deployments on the Pro plan, the backend hosting BAA is included. No separate hosting account or BAA negotiation required. After deployment, Specode doesn't store or access your patient data.
Only Replit, via React Native/Expo. Lovable, Blaze, and Specode produce responsive web applications that work on mobile browsers but don't generate native iOS or Android apps.
Blaze and Specode offer native FHIR/HL7 support and named EHR integrations. Replit and Lovable can technically call FHIR APIs through custom code, but since neither can handle PHI in production, any real EHR data flowing through them would violate HIPAA.
Specode's Pro plan — describe your healthcare workflow to the AI builder, implement compliance features with its guidance, and deploy on infrastructure with an included hosting BAA. Blaze is also production-ready for HIPAA but requires enterprise pricing and sacrifices code ownership.