Is Lovable HIPAA Compliant?

Updated October 2026
No. Lovable's current Enterprise documentation says it doesn't sign BAAs and isn't HIPAA compliant. Its Business and Enterprise DPA also prohibits PHI.
Built your app in Lovable? We migrate Lovable prototypes to a HIPAA-ready stack with a signed BAA, and you keep your UI. Migrate my Lovable app
Last verified: October 30, 2026.
We hear "is Lovable HIPAA compliant" after a founder's prototype has already won buy-in. The screens work. Now the production data path needs its own review.
Can a HIPAA-enabled backend cover a Lovable app?
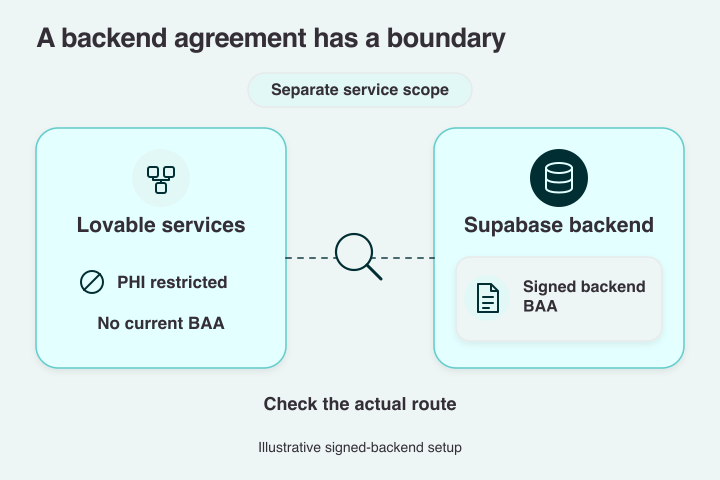
A Supabase BAA covers the agreed backend scope. Lovable's own PHI restrictions still apply to its services, and its Enterprise docs say it doesn't currently sign BAAs. Review the complete workflow before real patient data enters it.
Key Takeaways:
- Lovable currently says it signs no BAA. Its Terms retain a written-permission exception, but there's no published Enterprise PHI pathway to recommend.
- Security settings cover different surfaces. Check prompts, project access, application authorization and connected services separately.
- Keep the prototype work you've proved. Specode moves Lovable apps onto a HIPAA-ready foundation while preserving reusable UI and application logic.
What Lovable's documents say
A Lovable HIPAA compliance review starts with the current agreements. The Terms were updated August 28, 2026, with an August 15 effective date.
The Terms qualify their PHI restriction with "Unless your plan or a separate written agreement with us", followed by a requirement for express permission. The standard service isn't intended for regulated sensitive-data recordkeeping.
That conditional wording hasn't become a published HIPAA offering. Lovable's Enterprise FAQ expressly says it doesn't currently sign BAAs. Upgrading to Enterprise or requesting a custom DPA doesn't establish an approved PHI route.
The Business/Enterprise DPA is more direct. Section 3.8 instructs customers "not to upload, input, or otherwise provide any protected health information under HIPAA". Its webpage and linked signed PDF show different November dates; both contain that restriction.
Read those documents together: the Enterprise FAQ supplies the current BAA answer, the Terms/DPA limit permitted data, and the Privacy Policy explains how content is used and retained.
| Document | Version or update date | HIPAA / BAA finding | Primary source |
|---|---|---|---|
| Terms of Service | Updated August 28, 2026; effective August 15, 2026 | PHI restriction with express-permission exception; no BAA offering | Terms |
| Business/Enterprise DPA | Webpage: November 6, 2025; signed PDF: November 17, 2025 | Section 3.8 prohibits PHI; no HIPAA BAA offering | DPA, signed PDF |
| Privacy Policy | Updated/effective September 15, 2026 | No HIPAA or BAA mention in the reviewed policy | Privacy Policy |
| Security page | No update date displayed; checked October 30, 2026 | No HIPAA or BAA mention in the reviewed page | Security |
For a covered entity or business associate, trace which providers create, receive, maintain or transmit ePHI. HHS cloud guidance explains the agreement requirement; our guide to what a BAA actually covers covers its scope.
Lovable's compliance guidance reports SOC 2 Type II attestation. Keep that assurance in the vendor review, alongside the explicit HIPAA answer and the application's own safeguards.
Inside Lovable: trace each PHI path
A Lovable.dev HIPAA compliance check has to follow the actual app. Current Cloud documentation describes a built-in backend with authentication, database, storage and functions. You can also connect your own Supabase project.
Start with prompts and attachments, then follow requests into the running app and its connected services. Inspect credentials that could reach a live patient system during a prototype test.
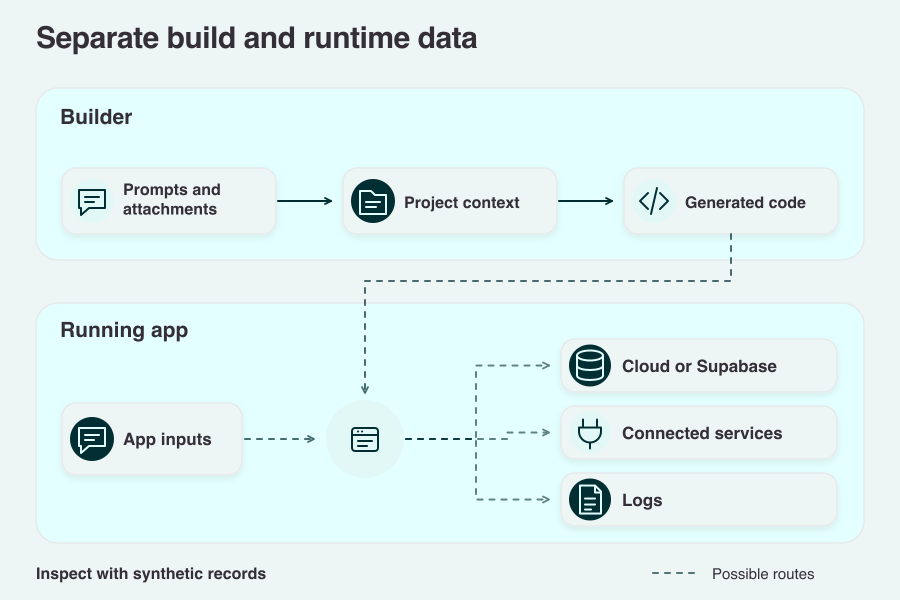
Check the auth service your app actually uses
Clerk is one possible provider, with a BAA available on its Enterprise plan. It isn't the documented default for every Lovable app. Check the actual identity provider, then test who can access each patient's records.
Use the HIPAA authentication requirements when reviewing the app's access controls. A successful login still leaves authorization and patient-access logging to inspect.
Confirm that the app records the patient-record access your review needs, beyond workspace activity.
Supabase needs its own covered setup
Supabase's HIPAA configuration requires Team or Enterprise, a paid HIPAA add-on and a signed BAA. Team starts at $599/month; the add-on and required configuration add to the bill.
Supabase also requires at least small compute for PITR. Its shared-responsibility guide leaves table access, RLS and database credentials with the customer.
Lovable can generate schemas and access policies through its Supabase integration. Verify those policies against the intended roles, alongside the provider's account and project settings.
Training controls now depend on the plan
Current data controls exclude Business and Enterprise workspace data from training by default. Free and Pro users can turn model training off in account preferences.
The opt-out applies going forward, without retracting content from earlier training datasets or models. Lovable's current Privacy Policy separately excludes app users' database/storage data from training. Treat training choice, retention and permission to process PHI as separate checks.
Quick and Deep scans check different risks
Lovable introduced Security Scan with Lovable 2.0 on April 24, 2025. In his May 2025 statement, Palmer criticized the early scan for checking whether RLS rules existed without establishing whether they matched the app's access requirements.
Its current security docs describe:
- Quick: automatic publish-time checks for database configuration and known dependency issues.
- Deep: application-code review, including access control and unauthenticated endpoints.
Lovable says these scanners don't guarantee complete security. Use their findings in the security review and inspect the remaining PHI paths.
The incidents had different failure paths
- 2025 database policies: Matt Palmer's CVE-2025-48757 disclosure concerned inadequate Supabase RLS. His follow-up statement reported 170 projects with inadequate RLS in a March scan. The CVE record records a supplier dispute over customer responsibility.
- February 2026 application authorization: The exposure was reported by Taimur Khan. He described inverted authorization in Supabase RPC functions and 18,697 user records accessible without login.
- April 2026 project permissions: Lovable's April 22 response says public-project code and chat were potentially accessible to authenticated users with a project link from February 3 through April 20. Private projects and Lovable Cloud weren't affected, according to Lovable. We cover the HIPAA angle on this one separately.
Test database rules, application authorization and project sharing independently. These reports don't establish that every current Lovable app leaks data.
Can you hack Lovable into HIPAA compliance?
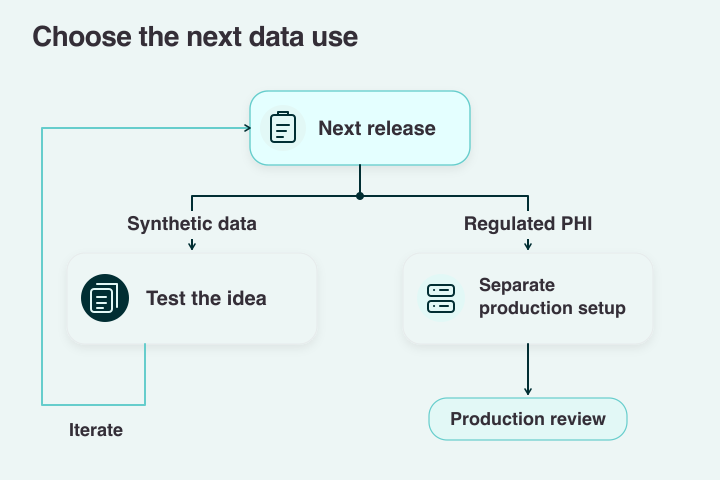
You can export generated code and prepare a separate production deployment. Lovable's current no-BAA position still governs PHI that reaches its services. Keep that boundary visible through the work:
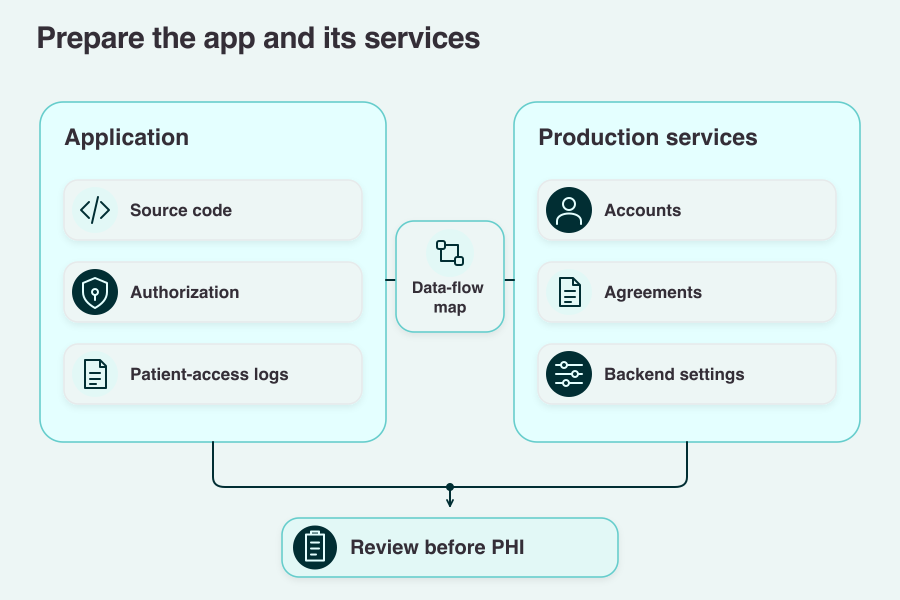
- Map the data path: inspect prompts and attachments as well as the running app. Keep real PHI out of unapproved development services.
- Choose covered production services: get the agreements for the services handling PHI.
- Supabase needs Team or Enterprise with the HIPAA add-on and signed BAA.
- Other providers need their own scope checked.
- Review authentication: confirm the actual provider and test authorization across patient and staff roles. Use the authentication checks discussed earlier.
- Configure the backend: for Supabase, enable High Compliance, PITR, SSL enforcement, network restrictions and connection logging. Test the RLS policies against expected access.
- Review development controls: set training preferences and check project access separately from published-app access. These settings don't grant PHI permission.
- Check the audit trail: review both:
- workspace events your platform records
- patient-record access recorded by the application
- Review and test before cutover: vet the code using synthetic data, prepare the destination and complete the production checks before introducing PHI.
Or skip the list. See the Lovable migration path →
How to prototype safely: Lovable without real PHI
Use the prototype to test workflows with entirely fabricated records. You can learn whether intake screens work or a clinician can find an appointment without copying a real patient chart into the builder.
Synthea generates synthetic patient histories. Faker supplies fake fields for test fixtures. Keep test inputs clearly separate from production records and credentials.
- Check project access: review who can open the editor and whether public remixing is allowed.
- Test the published app: try its endpoints without authentication, then check access across different user roles.
- Inspect outputs: use synthetic inputs to see what enters logs, URLs, exported files and connected services.
- Review credentials: confirm that test connections can't reach a live patient system.
Project privacy and database access policies protect different surfaces. Test both. Lovable documents Enterprise workspace audit logs and backend logs; the application still needs an appropriate patient-access trail.
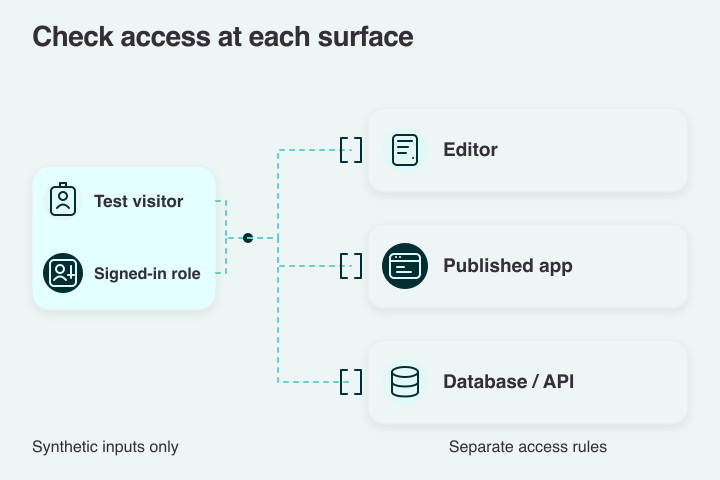
If you use transformed real records, follow an accepted de-identification method. Removing a few identifiers doesn't make the result synthetic.
For GDPR, Lovable's October 2026 guidance leaves application-specific data handling with the app owner. Review that privacy workflow alongside the platform's commitments. A GDPR DPA doesn't grant HIPAA permission for PHI.
Move a Lovable prototype to Specode
Keep the product decisions you've already made. We read the existing code, map the screens and data model, and repurpose the application on a HIPAA-ready foundation. Your UI and reusable business logic come with it.
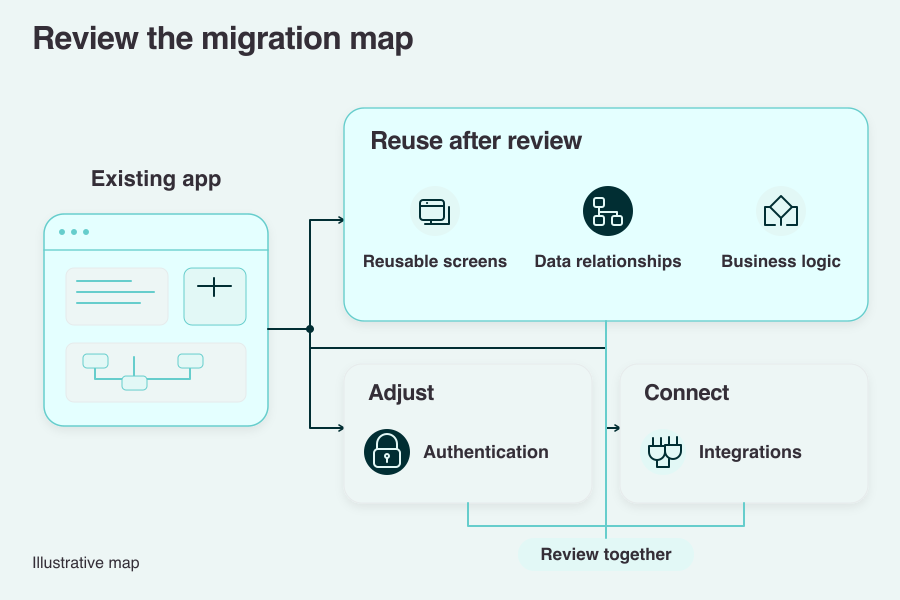
Describe the patient intake or video-visit workflow you need, and Specode writes the code around it. Scheduling and EHR connections can grow from that foundation, with external services connected for the job you've scoped.
You own the application code. Export it whenever you want. You can modify it yourself or take development in-house.
Specode's terms also prohibit using customer code, data, prompts or apps to train, fine-tune or benchmark AI models, including aggregated or de-identified content.
The Maestro build workflow guides planning, design and implementation. The HIPAA Compliance Agent finds potential code-level issues and supports the fix-and-recheck work.
Production uses your own Convex account, with a hosting BAA signed directly with Convex. Our team helps with deployment and a pre-launch security/HIPAA review, typically 1-2 business days. Use synthetic data in the builder and previews.
Review the project map before work starts. See which screens and relationships can transfer, then check what authentication and integrations need before the move. The migration stays tied to the app you've built.
Our migration guide explains the review process. Keep shaping the care workflow, with the UI you've tested and application code you own.
Lovable vs. Specode: choose the PHI path
For the wider field, we compare Specode against Replit, Bolt, and Blaze too. The dedicated reviews Is Bolt HIPAA compliant and Is Base44 HIPAA compliant cover those platforms.
| Decision | Lovable | Specode |
|---|---|---|
| HIPAA / BAA | Currently says it signs no BAA | HIPAA-ready foundation; production hosting under a signed BAA |
| PHI environment | Keep PHI out of its platform workflows | PHI restricted to prepared production; synthetic builder/previews |
| Speed | Prompt-to-app prototyping | 3-5-screen prototype around 10 minutes; basic telehealth production estimate 1-2 weeks |
| Builder and preview | Built-in Cloud/auth or connected backend; Quick/Deep security checks | Healthcare-focused generation and shareable preview |
| Code and training | Exportable code; plan-based training controls | Full code ownership; no training on customer content |
| Integrations | Custom APIs; verify each provider's scope | Describe the workflow and connect the services it needs |
| Iteration | Automated security checks and guided fixes | Auto-saved build history, rollback and example role logins |
| Branding | Conversational design changes | Conversational branding and full UI control |
| Cost | Supabase Team starts at $599/month, plus paid HIPAA add-on and other charges if chosen | Pro: $1,000/month; third-party accounts and charges are separate |
| Use | Healthcare prototyping with synthetic data | Production healthcare apps, including telehealth and patient intake |
Our HIPAA compliant app builder buyer's guide covers the category. If you're asking is Lovable HIPAA compliant, you can keep the UI you've proved and move onto a healthcare foundation. For a comparison of prototype workflows before migration, see lovable vs replit for healthcare apps.
Your Lovable prototype, production-ready for PHI
- Code ownership: keep your application code and export it whenever you want.
- BAA: production hosting under a signed agreement.
- Timeline: Specode advertises a 3-day migration to a HIPAA-ready foundation; scope and production timing depend on your app.
Frequently asked questions
Lovable's current Enterprise documentation says it doesn't sign BAAs and isn't HIPAA compliant. Recheck that published position before selecting services for PHI.
Lovable supports custom API integrations. Check the particular EHR's interface, permissions and PHI path; API access alone doesn't establish permission for patient data.
Use entirely fabricated records and test project access separately from app authorization. Code export can preserve your work when preparing a different production deployment.
Assess where the PHI traveled and follow your organization's incident-response process. Changing training preferences doesn't erase earlier exposure or prove the data was deleted.
Describe the service and workflow, supply required credentials, and Specode helps build the API connection. Validate the external provider's requirements before using PHI.
Connection is possible. Team or Enterprise, paid HIPAA add-on, signed BAA and project configuration cover backend eligibility. Lovable's own PHI restrictions still apply.